Mortgage Compliance Policies and Procedures Guide
Reglith Editorial Team · October 2026
A mortgage compliance policy states what the institution requires; a procedure states who does it, when, and with what evidence. Together, written compliance policies and procedures translate Regulation Z, RESPA, HMDA and SAFE Act obligations into repeatable steps that staff can follow and examiners can test. The framework only works when policies are current, specific to the institution's business model, and verified through monitoring.
Building a Mortgage Compliance Management System (CMS): Policies, Monitoring, Audits, and Regulatory Change explains how those documents sit inside the broader CMS.
What are the core components of a mortgage compliance policy framework?
A policy is a governance statement: it names the legal requirement, assigns accountability, and sets the institution's risk tolerance. A procedure is execution detail: the sequence of steps, the system of record, the timing, and the evidence retained. Lenders that blur the two end up with documents too vague to audit or too granular to maintain.
The primary regulatory drivers for mortgage lending include:
- Regulation Z, 12 CFR 1026 — disclosure timing and content, including the TRID integrated disclosures at 12 CFR 1026.19, loan originator compensation, and ability-to-repay standards.
- RESPA and Regulation X, 12 CFR 1024 — settlement services, escrow, and servicing and loss mitigation requirements.
- HMDA and Regulation C, 12 CFR 1003 — requires financial institutions to collect data on covered loan applications received, covered loans originated, and covered loans purchased for each calendar year, and to record and report that data as the regulation specifies.
- The SAFE Act and NMLS — registration and licensing of mortgage loan originators, including state-specific licensing through NMLS.
The Compliance Management System (CMS) is the structure that houses these documents, along with training, monitoring and audit. The complete guide to federal mortgage compliance regulations maps the wider rule set that policies must reflect.
Policies must fit the institution. A depository and a nonbank mortgage company have different charter obligations, supervisory agencies and investor requirements. Size, product mix (forward, reverse, construction, servicing-retained versus released), and state footprint all shape what belongs in the document set.
How do you ensure compliance with policies and procedures in daily operations?
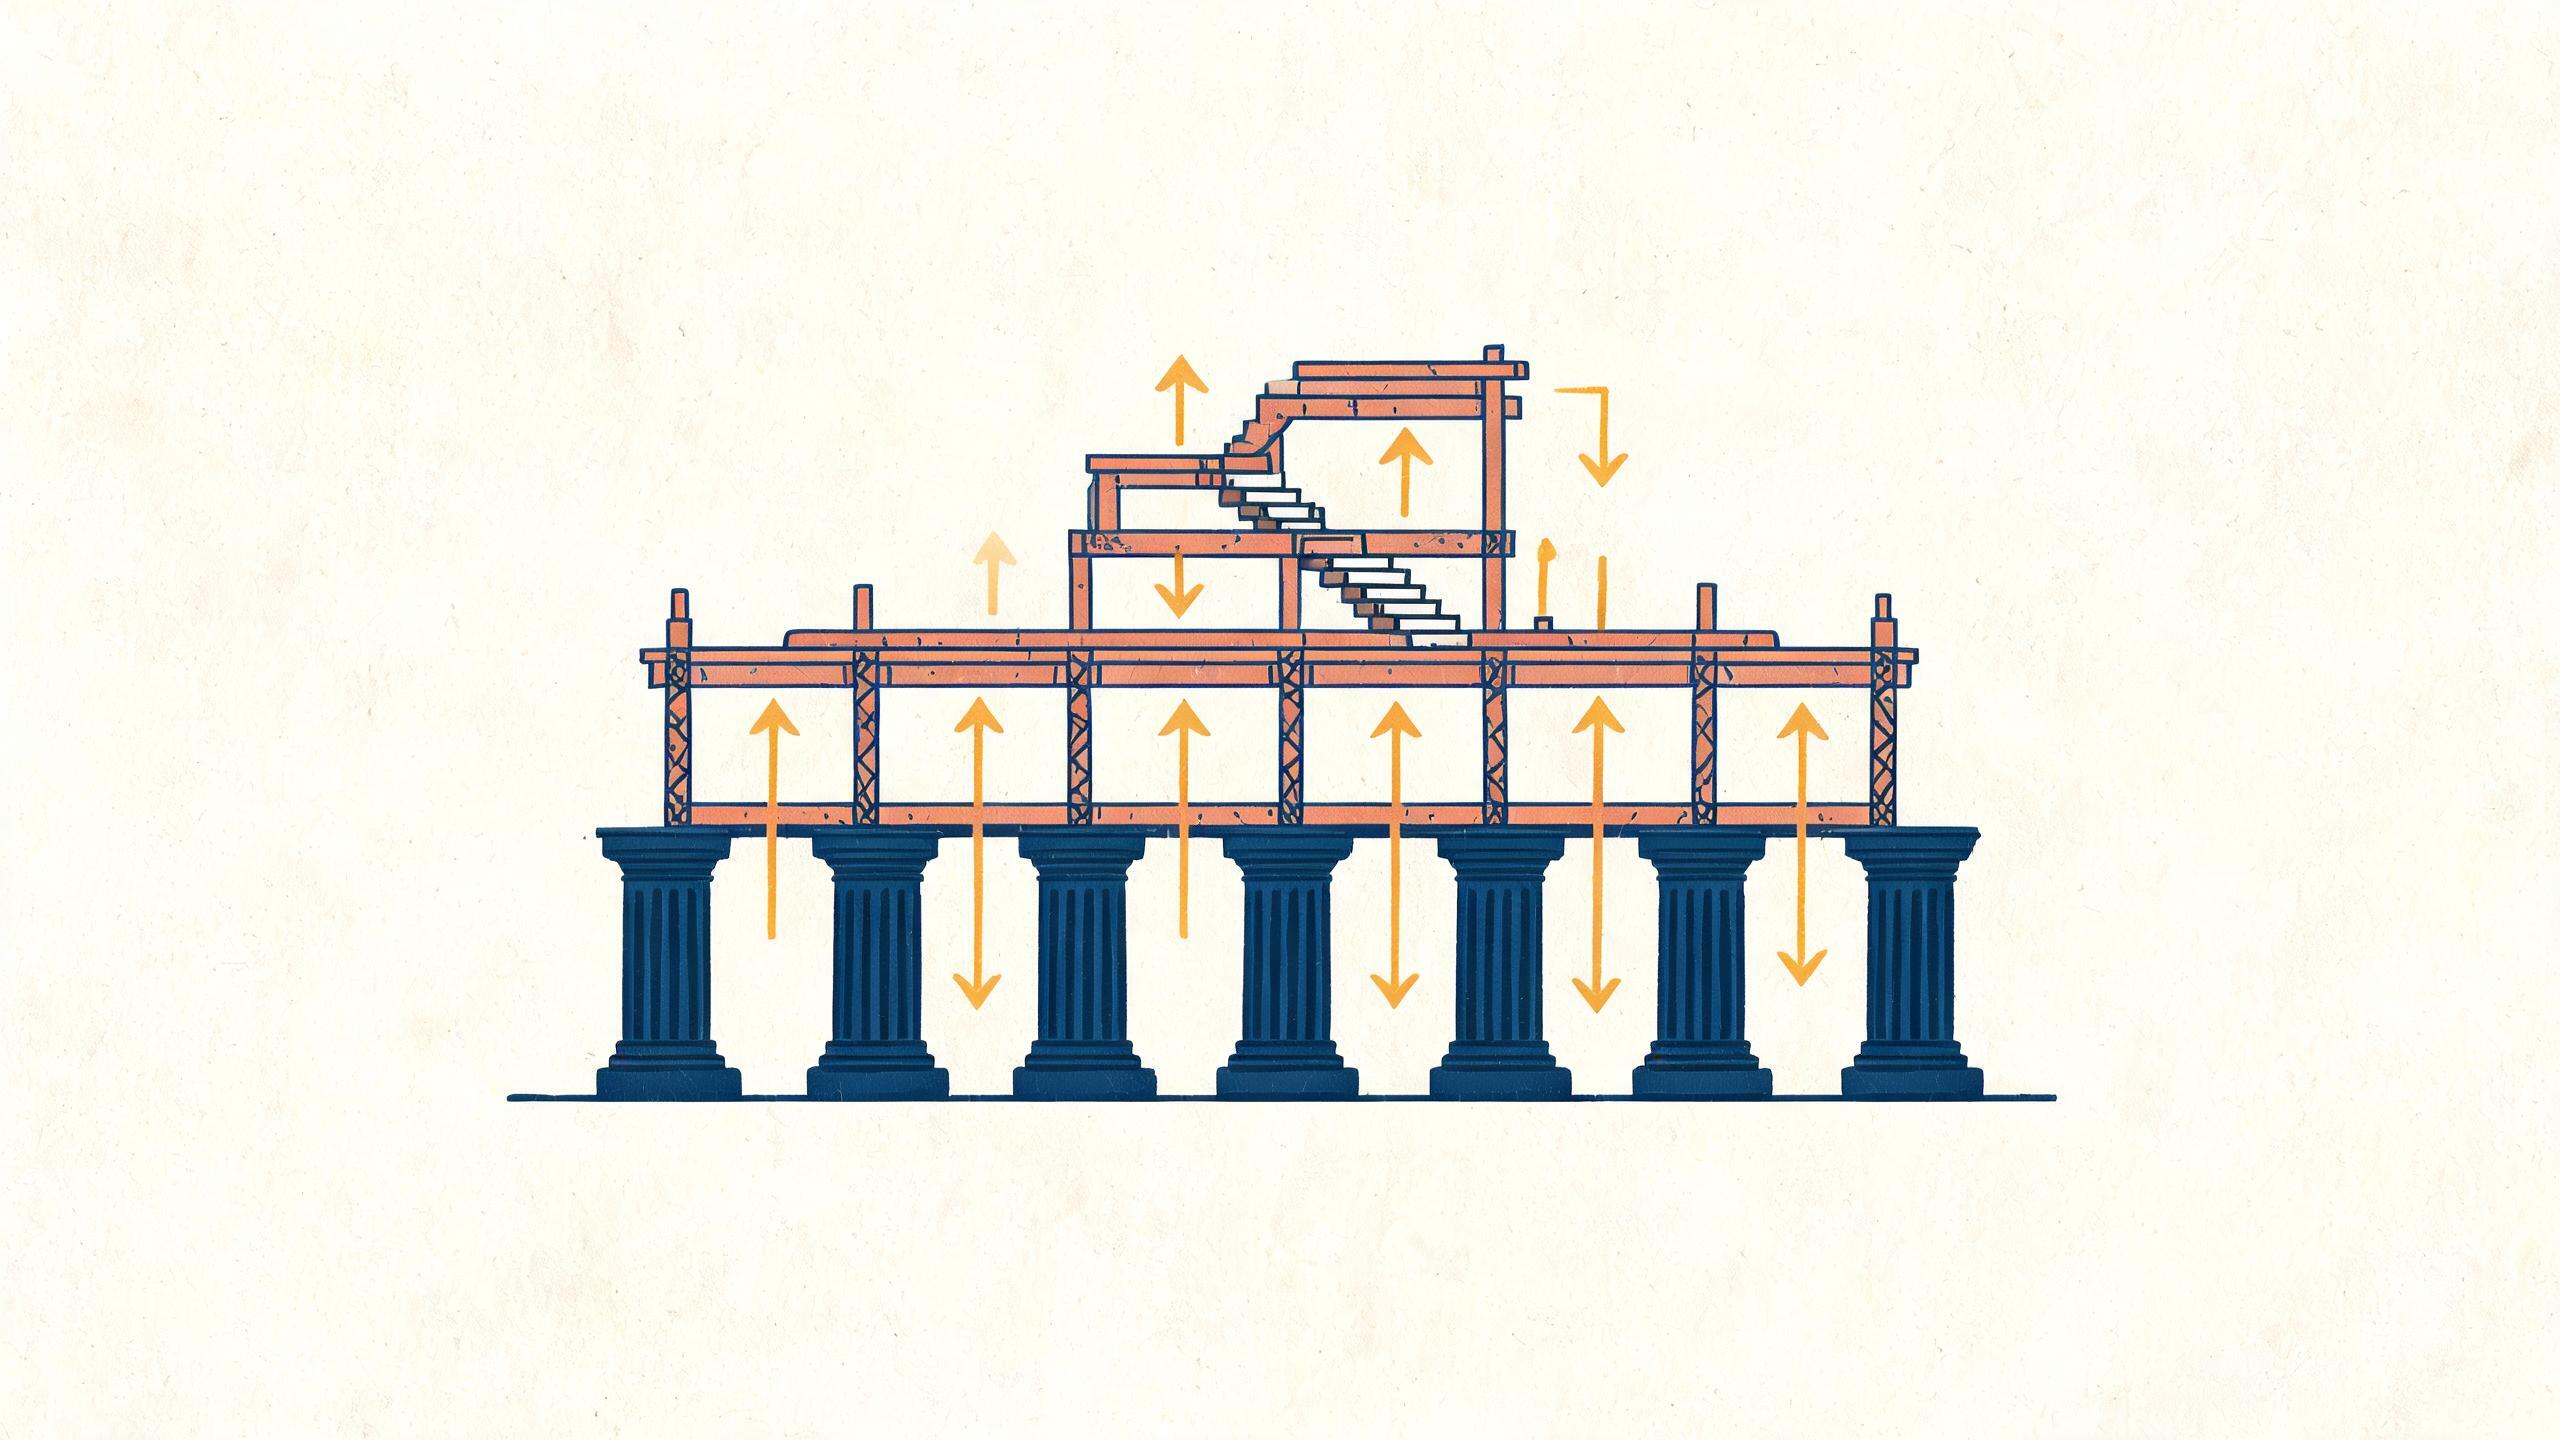
Written rules do not enforce themselves. The practical goal is making the compliant path the default path in the loan origination system and workflow tools — required fields, hard stops at disclosure deadlines, and checklists that cannot be skipped.
Role-based training is the second control. Loan officers, processors, closers and servicing staff need training keyed to the procedures they actually perform, with completion tracked and, where the institution requires it, certification. Generic annual training rarely demonstrates that staff understood the procedure.
Monitoring and testing close the loop. Monitoring is ongoing surveillance of operational data; testing samples files against written criteria to confirm the procedure was followed. Both produce findings that feed corrective action.
Escalation paths matter most when something goes wrong. Staff need a defined route for exceptions, deviations and potential violations — one that reaches compliance without requiring them to guess whether an issue is serious.
What are the 5 pillars of an effective compliance program?
Regulators commonly describe an effective compliance program through five elements, sometimes called the five pillars:
- Written policies and procedures — the documented requirements.
- A designated compliance officer or function — with authority and independence.
- Training — tailored to roles and risk.
- Monitoring and auditing — periodic testing of adherence.
- Corrective action — consumer remediation and process fixes when gaps are found.
The CFPB and the OCC, along with the FDIC and Federal Reserve for the institutions they supervise, describe these elements with different emphasis in their supervision and examination materials. The pillar framing is a common heuristic; specific citations vary by agency and by supervisory manual, so teams should read the current examination guidance for their charter.
Each pillar depends on the others. Policies without training go unread; training without monitoring is unverified; monitoring without corrective action produces findings that never close.
| Element | Best for | Notes |
|---|---|---|
| Policies and procedures | Establishing the standard | Must be specific enough to test |
| Training | Building staff capability | Role-based beats one-size-fits-all |
| Monitoring | Detecting drift between policy and practice | Ongoing, data-driven |
| Audit and testing | Independent verification | Samples files against criteria |
| Corrective action | Closing gaps | Includes remediation and root-cause review |
How should institutions manage regulatory changes within their policies?
Regulatory change management is the process that connects a new or amended rule to the policies it affects. It typically starts with identification — tracking the Federal Register, eCFR, agency bulletins and state regulator notices — and moves to impact assessment: which products, states, systems and vendors does this touch?
From there, the workflow is drafting, review and approval. Legal and compliance review the redline; business owners confirm operational feasibility; a designated approver signs off. The change is then communicated to staff and, where relevant, to service providers, with training updates where the change affects procedures.
Version control is not administrative housekeeping. Examiners and internal auditors will ask which version of a policy was in force on a given date. Dated versions, approval records and a change log create the audit trail that answers that question.
What role do service providers play in policy compliance?
Service provider oversight extends the institution's compliance expectations to third parties. That begins in the contract: compliance provisions, audit rights, reporting obligations and termination remedies set the baseline for what a vendor must do.
Ongoing oversight includes periodic assessments, reviewing vendor attestations and, for higher-risk relationships, conducting or commissioning audits. Vendor risk should be tiered — a document custodian and a marketing vendor do not carry the same compliance exposure.
The lender remains responsible for the compliance of work performed on its behalf. A vendor's failure is generally the institution's finding in an examination, which is why oversight is a policy obligation rather than a procurement detail.
How do you test the effectiveness of compliance policies?
Monitoring and testing are related but distinct. Monitoring watches operational data continuously — disclosure timing reports, HMDA data validations, licensing status checks. Testing samples individual files to determine whether the written procedure was actually followed.
A mortgage compliance testing program defines scope, sample selection methodology, testing criteria and reporting. Samples are usually drawn to cover product types, channels, states and staff. Pre-funding quality control review acts as a first line of defense, catching disclosure and documentation issues before the loan closes.
Findings need a remediation process: root-cause analysis, assignment of ownership, a target date, and verification that the fix worked. The compliance audit guide for mortgage servicing covers testing design in the servicing context.
What are common examples of mortgage compliance policies?
Common compliance policies examples include a TRID and Regulation Z disclosure policy, an HMDA data collection and reporting policy, a RESPA servicing and escrow policy, a fair lending policy, and a SAFE Act licensing policy. The fair lending compliance guide and the mortgage licensing and NMLS guide address those areas in depth.
The translation from policy to procedure is concrete. A policy stating that disclosures must be delivered within Regulation Z timing requirements becomes a procedure: the system generates the disclosure, a tracking report lists delivery dates, a designated reviewer checks the report against the deadline, and exceptions are logged and escalated.
The CFPB's supervision and examination process reviews these documents for evidence that the institution identified its risks and built controls proportionate to them. Issues that do not rise to a violation are often documented as matters requiring attention, which then need tracking to closure.
Frequently asked questions
Can you give me an example of a compliance policy?
A disclosure timing policy is a common example. It references Regulation Z, 12 CFR 1026, states the institution's standard for delivering the Loan Estimate and Closing Disclosure within required timeframes, assigns responsibility to a named function, and requires a tracking report with documented exception review.
What are the 5 pillars of compliance?
The five pillars are commonly described as written policies and procedures, a designated compliance officer or function, training, monitoring and auditing, and corrective action. The CFPB, OCC, FDIC and Federal Reserve describe these elements with varying emphasis in their examination materials; the framing is a heuristic, not a single uniform citation.
What are the 7 elements of compliance?
Some frameworks expand the five pillars into seven elements, often separating governance and oversight, consumer complaint handling, and third-party oversight into standalone items. The specific list varies by source, so teams should anchor on their primary regulator's examination guidance rather than a single published list.
What are the three 3 C's of compliance?
The three C's are commonly cited as commitment, culture and communication — or, in some versions, compliance, controls and culture. The framing is informal and not tied to a regulatory citation; it is useful for training and tone-at-the-top discussions rather than as an examination standard.
How often should compliance policies be reviewed?
Many institutions set an annual review cycle with interim updates triggered by regulatory change, audit findings or business changes. No single federal rule sets a universal interval for all policies; the appropriate cadence depends on the institution's risk profile, charter and supervisory expectations.
Who is responsible for approving compliance policies?
Approval authority is typically assigned by board or management governance: the board or a board committee approves high-level policies, while functional management approves operational procedures. The specific allocation varies by institution and charter, so it should be documented in the governance framework itself.